
A compliance team that can review 200 KYC files a week by hand looks fine at 150 signups a month. The same team looks broken at 5,000. Nothing about their process changed; the volume moving through it did, and spreadsheets and manual review queues don’t scale the way engineering infrastructure does. This is the part of RegTech adoption that founders tend to miss until it’s already a problem: the question was never whether to automate compliance. It was when the math stopped working.
Why Manual Compliance Breaks Down Before Manual Processes Do
A manual KYC queue, a shared spreadsheet tracking suspicious activity flags, a compliance officer who reviews transaction alerts between meetings: these work when volume is low enough that one person can hold the whole picture in their head. The failure isn’t dramatic. It’s a backlog that grows a little each week until onboarding takes three days instead of three minutes, or a suspicious transaction that sits in a queue for 48 hours because nobody got to it in time.
The math is straightforward. If transaction volume grows linearly and your review capacity is fixed, your backlog grows without bound. Adding headcount buys you a higher ceiling, not a different curve. At some transaction volume, every fintech hits the point where manual review can no longer keep pace with inflow, and the gap between what’s coming in and what’s getting reviewed starts to compound.
This is also where risk changes shape. A missed suspicious activity report at low volume is one incident. At higher volume, with a backlog, it’s a pattern, and regulators treat patterns very differently than they treat incidents.
What RegTech Actually Automates: KYC, AML, and Transaction Monitoring
RegTech isn’t a single tool. It’s a category covering several distinct compliance functions, each of which has its own manual version and its own automated replacement.
KYC (Know Your Customer) automation verifies identity documents, cross-checks them against databases, and screens customers against sanctions and watchlists, in seconds rather than the hours or days a manual reviewer needs per file. The system doesn’t get tired on file 400 the way a human reviewer does.
AML (Anti-Money Laundering) monitoring automates the screening that used to require a compliance analyst manually checking a customer or transaction against sanctions lists and politically exposed person databases. Automated AML tools run that check continuously, against lists that update constantly, which a manually maintained spreadsheet simply cannot do.
Transaction monitoring is where automation does the most work. Instead of someone periodically pulling transaction reports and eyeballing them for anomalies, automated monitoring evaluates every transaction as it happens against a set of rules and risk models, flagging only the ones that need human attention. This is close kin to the fraud detection problem: the same shift from static rule-checking to continuous, model-driven evaluation that shows up in how machine learning catches fraud that rule based systems miss is happening in parallel inside transaction monitoring, because both problems are really the same problem: too many events, not enough human attention, and patterns that change faster than a rulebook can be rewritten.
The common thread across all three is that RegTech doesn’t eliminate judgment. It eliminates the repetitive, high-volume screening that judgment shouldn’t have to be spent on, so that the humans on a compliance team are reviewing the handful of cases that actually need a person, not the thousands that don’t.
From Periodic Checklists to Continuous, Real-Time Compliance
The older model of compliance was periodic by design: quarterly audits, monthly reconciliations, batch-reviewed transaction reports. That model made sense when the underlying infrastructure it monitored was also periodic. Batch-processed payments settled on a schedule, so compliance checks ran on a schedule too.
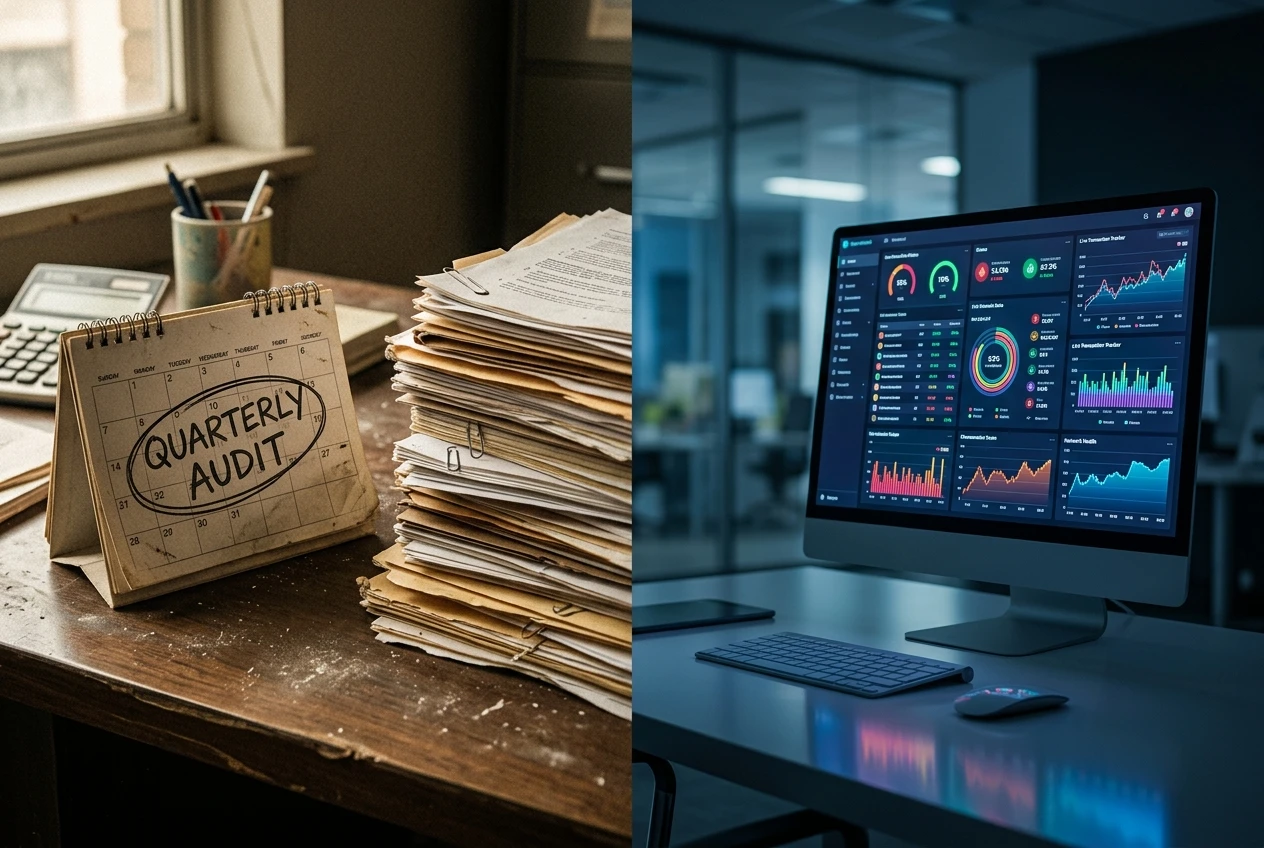
Real-time payment rails changed the underlying assumption. When money moves and settles continuously, as covered in real-time payment settlement best practices, a compliance process that only checks in once a quarter is reviewing activity that’s already weeks or months old by the time anyone looks at it. A quarterly audit catches a problem after it’s had a quarter to compound.
Continuous compliance monitoring doesn’t just run more often. It runs differently: every transaction, every onboarding event, every change in customer risk profile gets evaluated as it happens, and the system maintains a running state of risk rather than reconstructing it periodically from historical data. The checklist model asks “were we compliant last quarter?” The continuous model asks “are we compliant right now?” and those are different questions with different infrastructure requirements.
Why Regulators Are Adopting the Same Automation (and What That Means for You)
Regulators have started building and using their own automated tools to analyze the data fintechs submit, and that shift has a direct consequence for how fintechs are expected to operate: a regulator running automated analysis on submitted data can detect patterns, gaps, and inconsistencies far faster than a human examiner working through paper filings.
That changes what “adequate” compliance looks like. A manually maintained audit trail with gaps and inconsistent formatting might have passed review when the reviewer was also working by hand. It stands out immediately against a dataset that regulatory systems are built to parse automatically. The baseline expectation has shifted from “can a person eventually verify this” to “can this be verified at machine speed,” and that shift applies whether or not a given fintech has automated its own side yet.
Banking partners have followed the same logic. A sponsor bank evaluating a fintech partnership is increasingly asking what compliance infrastructure is in place, not just what policies are written down. Automated, auditable, real-time compliance has become table stakes for that conversation rather than a differentiator, which is a meaningful shift from where the expectation sat even a few years ago.
The Hidden Cost of Staying Manual: Headcount, Delays, and Audit Risk
The most visible cost of manual compliance is headcount. Every doubling of transaction volume under a manual model tends to require a corresponding increase in compliance staff just to hold the backlog steady, and that’s a cost that scales with growth rather than shrinking as a company matures.
The less visible costs usually matter more. Onboarding delays caused by manual KYC review push away customers who expected a same-day signup. A backlog of unreviewed transaction alerts is a liability sitting on the books, not a line item. And audit risk compounds quietly: a manual process that depends on a specific analyst remembering to check a specific list is a single point of failure, and regulators don’t treat “our analyst missed it” as a satisfying answer during an examination.
There’s also an opportunity cost that’s easy to underweight. Every hour a compliance team spends manually reviewing files that an automated system could screen is an hour not spent on the cases that genuinely need judgment, like an ambiguous transaction pattern or a borderline customer risk profile. Staying manual doesn’t just cost more in salary. It redirects your best compliance judgment toward low-value repetitive work and away from the decisions that actually need it.
Where to Automate First If You’re Still Running Compliance by Hand
If a compliance stack is still largely manual, the order of automation matters more than trying to automate everything at once.
- Start with KYC onboarding. It’s the highest-volume, most repetitive part of the stack, and automated identity verification tools are mature and widely available, which makes this the fastest win with the lowest integration risk.
- Move to sanctions and watchlist screening next. These lists update frequently, and a manually maintained check is a stale check by definition. Automated screening against continuously updated lists closes a gap that’s easy to overlook until it’s an incident.
- Automate transaction monitoring once volume justifies it. This is a heavier lift than KYC automation, since it usually requires tuning risk models and thresholds to your specific transaction patterns, but it’s also where the backlog risk described earlier shows up most directly.
- Build the audit trail into the automation itself, not around it. A system that logs every automated decision and every human override gives you something a manual process never did reliably: a complete, timestamped record that a regulator or banking partner can review without a reconstruction project.
Each of these overlaps with infrastructure decisions a growing fintech is already making elsewhere, from the identity verification layer discussed in biometric authentication in fintech to the scalability questions covered in cloud architecture for fintech scalability. Compliance automation isn’t a separate system bolted on afterward. It works best when it’s built into the same infrastructure decisions a fintech is already making to handle growth.
If you’re still working out which compliance obligations actually apply at your current stage, before deciding what to automate and in what order, see a founder’s roadmap to fintech compliance for a stage-by-stage breakdown.