
Fintech apps hold two things that attract criminals more reliably than almost anything else online: money and the personal data needed to move it. A social media breach exposes photos and messages. A fintech breach exposes account numbers, balances, and a direct path to someone’s savings. That difference changes the entire threat model, and it’s why a security approach borrowed from a typical SaaS app will leave gaps that attackers find quickly.
This piece walks through fintech app security best practices in the order they actually belong in a build, not as a list of buzzwords to check off. Encryption, authentication, API protection, testing, compliance, and incident response all depend on each other, and building them in the wrong sequence creates rework that costs more than doing it right the first time.
Why fintech apps draw more attackers than the average app
A fintech app is a more valuable target than most software for a simple reason: the payoff for a successful attack is direct and liquid. Stolen retail credentials might get resold for a few dollars. A compromised fintech account can be drained, used to launder funds, or sold as a verified identity with a transaction history attached.
Fintech apps also tend to integrate with more third parties than a typical app: payment processors, banking APIs, identity verification services, card networks. Each integration is a potential entry point, and attackers know that smaller fintech companies often move fast on features and slower on securing the connections between them.
Regulators have also raised the cost of getting this wrong. A breach at a fintech company doesn’t just mean reputational damage; it can mean fines, mandatory audits, and in some cases, a forced halt to operations until the problem is fixed. Building security into the roadmap from the start is cheaper than retrofitting it after an incident forces the issue.
Encrypting data at rest and in transit without tanking performance
Encryption is usually the first item on every fintech security checklist, and for good reason: it’s the baseline that makes every other control meaningful. But the common mistake is encrypting everything the same way and then wondering why the app feels sluggish.
Data at rest, meaning anything stored in your database, file storage, or backups, should be encrypted using strong, industry-standard algorithms. Most managed database services now offer this as a built-in option, which removes a lot of the implementation burden. The decision that actually matters here is key management: where encryption keys live, who can access them, and how often they rotate. A well-encrypted database with poorly managed keys offers little real protection.
Data in transit, meaning anything moving between the app, your servers, and third-party APIs, needs to run over TLS with current protocol versions. Older versions have known weaknesses, and keeping them enabled for compatibility reasons is a common and avoidable mistake.
The performance concern is legitimate but often overstated. Modern encryption, implemented with hardware acceleration and proper key caching, adds latency measured in milliseconds, not seconds. The places where encryption actually slows an app down are usually architectural: encrypting and decrypting the same data repeatedly in a request chain instead of once at the boundary, or using an outdated cipher suite that wasn’t built for current hardware. Fix the architecture before deciding encryption itself is the problem.
Choosing an authentication model: passwords, biometrics, and MFA done right
Authentication is where most fintech apps either build trust or lose it in the first ten seconds of use. The model you choose has to balance security against friction, because an authentication flow that’s too heavy will push users toward weaker workarounds, like writing passwords down or reusing them across accounts.
Passwords alone are no longer defensible for an app that moves money. If you still require them, enforce length over complexity: a long passphrase is harder to crack than a short string of mixed characters that’s awkward to type and easy to forget. Pair this with a password manager-friendly flow rather than fighting against autofill.
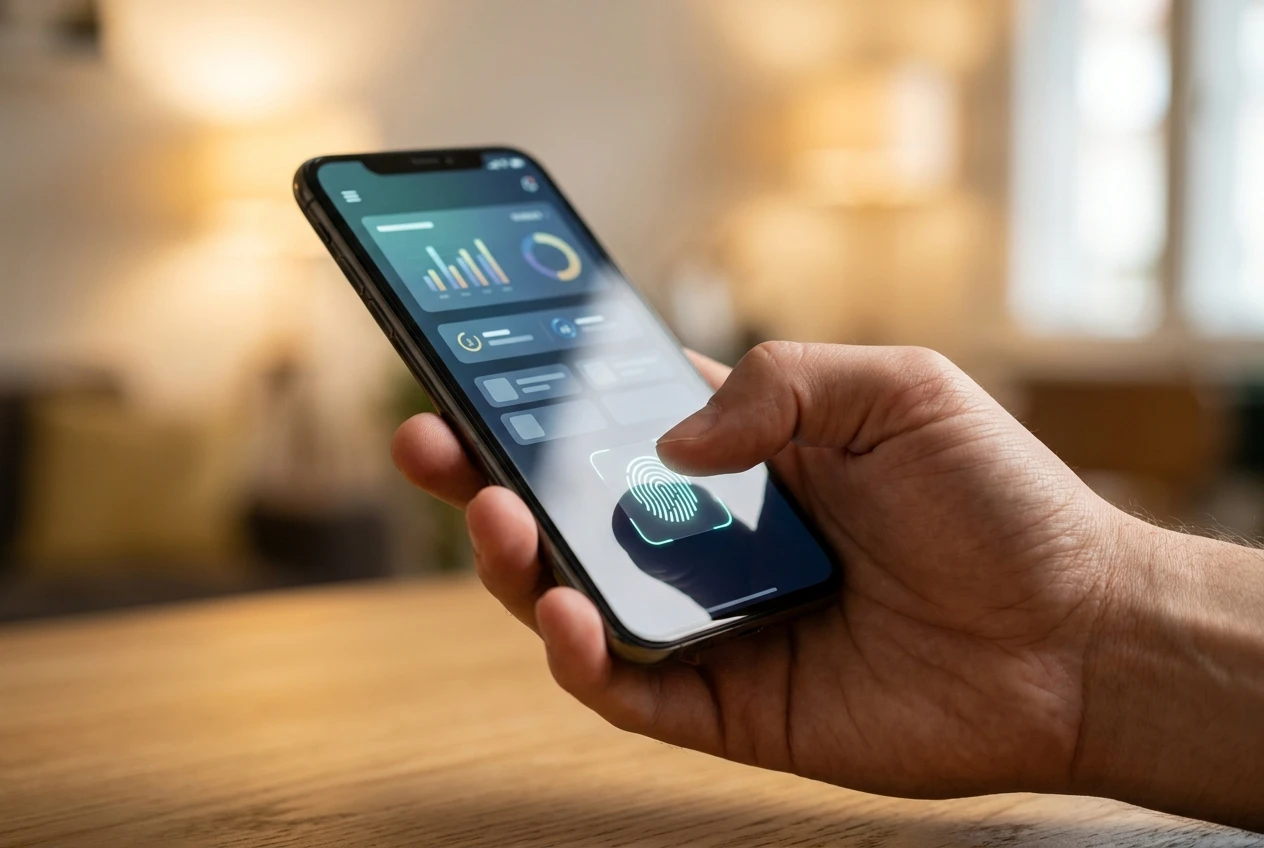
Biometric authentication, fingerprint or face recognition on the device, offers a strong usability and security trade-off for returning users. It’s fast, it’s hard to phish, and most users already have it enabled on their phones for other apps. The caveat: biometrics should unlock a local credential, not replace server-side authentication entirely. The biometric check confirms the right person is holding the device; it shouldn’t be the only thing standing between that device and a bank account.
Multi-factor authentication done right means layering something the user knows or is with something they have, applied at the moments that matter most: login from a new device, a password reset, a large transaction, or a change to account details. Requiring a second factor on every single action trains users to approve prompts without reading them, which defeats the purpose. Save MFA prompts for the moments where a real risk decision is being made.
Locking down the APIs that move money (and where payment gateways fit in)
APIs are where a lot of fintech security work either happens or gets skipped, because APIs are invisible to end users and easy to deprioritize under a deadline. They’re also the most direct route to a company’s money and data, which makes them the part attackers probe first.
Every API endpoint that touches a balance, a transaction, or personal account data needs its own authentication and authorization check, independent of whatever happened earlier in the user’s session. A common failure pattern looks like this: a user authenticates once, and every subsequent API call is trusted because it came from an authenticated session, without re-checking whether that specific user is allowed to access that specific resource. This is how one user ends up able to view or modify another user’s account data, simply by changing an ID in a request.
Rate limiting matters here too. Without it, a single compromised credential can be used to hammer an endpoint, testing account numbers or attempting transactions until something works. Rate limiting by user, by IP, and by endpoint type (login attempts should be limited more aggressively than read-only requests) closes off a large category of automated attacks.
Payment gateways deserve a specific mention because they sit at the exact point where a security failure turns into a financial loss. A payment gateway handles the sensitive work of moving card or bank data between your app and the financial networks that process it, which is also why using a reputable, PCI-compliant gateway rather than building payment handling in-house is one of the highest-leverage security decisions a fintech founder makes. If you want the full mechanics of what happens between a user clicking “pay” and the funds actually settling, this breakdown of how payment gateway APIs work walks through the handoffs in detail, and understanding those handoffs makes it much easier to see where your app’s responsibility for security starts and stops.
Where penetration testing actually belongs in your build cycle
Penetration testing gets treated as a box to check right before launch, which is close to the worst time to do it. Issues found at that stage are expensive to fix because the architecture is already set, and the pressure to ship on schedule makes it tempting to patch around a vulnerability instead of fixing its root cause.
The better placement is earlier and recurring. A focused penetration test after the core authentication and payment flows are built, but before the full feature set is finished, catches structural problems while they’re still cheap to fix. A second round before a major launch or after a significant architecture change, like adding a new payment method or opening up a new API for partners, catches what changed since the last test.
Between formal penetration tests, automated vulnerability scanning on every deployment catches the more routine issues: outdated dependencies, misconfigured permissions, exposed debug endpoints that should never have made it to production. This doesn’t replace a human tester probing for logic flaws, but it stops the easy stuff from piling up between the scheduled tests.
For an early-stage team, the realistic cadence looks like: a scoped test before the first real launch, automated scanning on every release after that, and a full penetration test at least annually or whenever the app takes on a meaningful new capability involving money movement or sensitive data. Treat it as part of the release cycle, not an event bolted onto the end of one.
The compliance frameworks that quietly set your security baseline
Compliance frameworks get a bad reputation for being paperwork exercises, but the better ones are actually a security roadmap in disguise, written by people who’ve seen a lot of fintech breaches and worked backward from the causes.
PCI DSS applies if you handle card data directly, and even if you route payments through a gateway specifically to avoid that scope, understanding the standard’s requirements around network segmentation and access control will shape decisions you’d otherwise make from scratch. SOC 2 is less about a specific checklist and more about proving that the security practices you say you follow are actually followed consistently, which matters enormously to enterprise customers and investors doing due diligence. Depending on your market, GDPR or similar regional data protection laws will set requirements around how personal data is stored, processed, and deleted, and building these in from the start is far less painful than retrofitting them once you have a live user base.
The useful way to think about frameworks isn’t “which one do we need to pass” but “which requirements in these frameworks are good practice regardless of whether anyone audits us.” Encryption key rotation, access logging, least-privilege permissions: these show up across nearly every framework because they’re genuinely effective, not because auditors like paperwork. Building to the spirit of the frameworks early makes the eventual audit a formality instead of a scramble.
Building an incident response plan before you ever need one
No security program prevents every incident. What separates a contained problem from a public disaster is usually how fast and how clearly a team responds in the first few hours, and that speed only comes from a plan written before anything goes wrong.
A workable incident response plan answers a short list of questions in advance: who gets notified first, who has the authority to take a system offline, what gets communicated to users and when, and what regulatory notification requirements apply to your specific situation. Writing these answers down during a calm Tuesday afternoon produces much better decisions than trying to figure them out while a breach is actively unfolding.
The plan should also include a clear log of what access each team member and system has, so that during an incident, you can quickly determine what was actually exposed rather than assuming the worst about everything. This is where the access controls and logging built earlier in the roadmap pay off directly: a system with granular logging turns incident response into a tractable investigation, while a system without it turns every incident into a guessing game.
Run through the plan at least once with the team before a real incident forces the issue. A short tabletop exercise, walking through a hypothetical breach scenario and talking through each step, reveals gaps in the plan: unclear ownership, missing contact information, assumptions about who has access to what. Finding those gaps in a rehearsal costs nothing. Finding them during a real breach costs trust, time, and in some cases, the business itself.
Security for a fintech app isn’t a single feature or a one-time audit; it’s a sequence of decisions that build on each other, from how data is stored to how a team responds when something goes wrong. Getting the order right, encryption and authentication first, APIs and testing next, compliance and incident planning running alongside the whole build, is what turns a list of best practices into an actual system that holds up under pressure.